This report is available in English and German; the page is shown in English.
Connected Products DACH 2027
Security is cheap. Waiting costs markets.
 Por
- Deadline24 hoursto the early warning on an actively exploited vulnerability
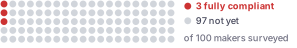
- Readiness3 %of surveyed makers consider themselves fully CRA-compliant
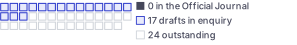
- Standards0 of 41requested CRA standards cited in the Official Journal
- Cost< €0.50security premium per device and month at 10,000 units
Why I wrote this
Since 2021 I have built connected products with RUBINLAKE for manufacturers who sell their machines and devices worldwide, from the radio module to the ERP. In almost every project the same question comes up, usually too late, once the hardware is fixed: what does security cost, and who pays for it? Until now nobody had a reliable number.
Since September 2026 the law has started answering the first half. The Cyber Resilience Act decides whether security belongs in the product. This report answers the second half with the figures our customers need for every architecture decision: what a secure device costs per month, which choices move that number, and which do not.
The short version is on the cover. Security is cheap. Waiting costs markets. The long version follows, with every source.
 Maxim BabarinowFounder and CEO, RUBINLAKE
Executive summary
In machinery and equipment, it is no longer only the factory that is connected but also the product that leaves it. The large majority of surveyed German makers of products with digital elements (94 %) already sell devices that can be updated in the field. Each of these devices extends the manufacturer’s responsibility beyond the factory gate and is a potential point of attack. The European Commission puts the damage its Cyber Resilience Act (CRA) could spare EU businesses at €180-290 billion a year.
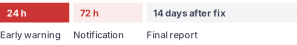
Europe has answered with five acts: the CRA, the Data Act, the Machinery Regulation, the cybersecurity rules of the Radio Equipment Directive and the Batteries Regulation. Between August 2025 and December 2027 they make security, updates and data access a condition of market access. The first duty already applies. Since 11 September 2026, manufacturers must report actively exploited vulnerabilities within 24 hours through ENISA’s single reporting platform.
The hardware of products launching in 2027 has to be fixed now. Yet no harmonised standard under the CRA or the Machinery Regulation is in the Official Journal, and no notified body has yet been designated under the CRA. Reliable cost figures are scarce, and few of the surveyed makers are ready. Whether security belongs in the product is no longer the manufacturer’s decision but the law’s.
to the early warning on an actively exploited vulnerability
of surveyed makers consider themselves fully CRA-compliant
requested CRA standards cited in the Official Journal
security premium per device and month at 10,000 units
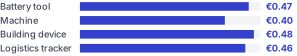
This report examines which design secures a connected product most cheaply over its life. It answers the question for manufacturers with 100 to 4,999 staff in Germany, Austria and Switzerland, using four typical devices: a battery tool, a machine with a gateway, a controllable building device such as a heat pump, and a logistics tracker. For these devices our cost model prices the base cost of radio and cloud and the security premium at list prices, in the base case for 10,000 units per product over five years. The security premium is small per device and about the same for every product. Unit volume, radio and backend decide the bill, and these choices are made before the standards arrive.
Main findings
- The obligations reach the installed base, not only new products.86 millionM2M SIM profiles in German networks, +17 % in one year
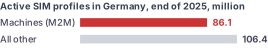
CRA vulnerability reporting has applied to installed devices since 11 September 2026.
- The Mittelstand is affected across the board, and readiness lags far behind.1,750-3,440makers in DACH, estimated
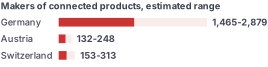
Only half of the surveyed German makers have started implementing the CRA.
- A gateway sold on its own has no route to conformity yet.0notified bodies under the CRA so far
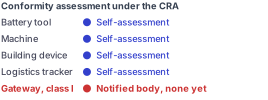
A class I gateway needs a notified body as long as no harmonised standard exists.
- Compliance is not what makes a connected product expensive.€0.50-3.10base cost and security premium per device and month
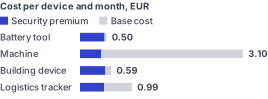
The radio and the backend decide the total, not security.
- Unit volume matters more than any component.€2.30security premium per device and month at 1,000 units
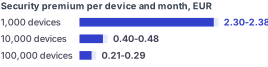
Fixed costs spread over all devices. The secure element is the smallest item.
- Tracker designs need a new battery concept and cellular without 2G.2028Germany's 2G networks close
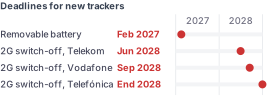
Most portable batteries must be removable by the user from 18 February 2027.
Manufacturers that settle architecture and backend now spread the cost of security over their whole fleet. Those that wait for the standards will design under deadline pressure, with fewer choices left. Chapters 1 to 7 set out the evidence, and Section 8 turns it into recommendations for the different roles in a company.
Free to read, share and quote. Citation required when you use it.
Contents
- 1Deadlines and scope11 min de lectura
- 2Device requirements16 min de lectura
- 3Cost per device7 min de lectura
- 4Technology and architecture22 min de lectura
- 5Spotlight: logistics tracking11 min de lectura
- 6Spotlight: Austria and Switzerland13 min de lectura
- 7Vendor landscape6 min de lectura
- 8Recommendations10 min de lectura
Anexos
Citation required
This report is free to read, share and quote. When you use figures, findings or text from it, cite it as:
Babarinow, M. (2026). Connected Products DACH 2027 (Version 1.1). RUBINLAKE GmbH. https://rubinlake.com/en/reports/connected-products